The U.S. CHIPS Act places explicit requirements on manufacturers regarding the traceability and authenticity of electronic components used in production. According to a white paper published in January 2025 by Cybord, a supplier of AI-driven component intelligence solutions, compliance demands go beyond supplier declarations and extend into the production process itself — including semi-finished goods and finished assemblies.
The paper identifies three core compliance pillars under the CHIPS Act: documented origin records for all electronic components, active verification processes for component authenticity, and adherence to established standards such as IPC-1752A for material declaration management and ISO 9001 for quality management systems. These requirements apply at every stage of the supply chain, not only at incoming goods inspection.
Cybord's central argument is that the predominant industry approach — relying on paper-based reports and supplier-provided documentation — constitutes a trust-based model that lacks technological ground truth. The company states that existing methods cannot reliably distinguish original components from counterfeits, remarked parts, or components with tampered markings, because verification is constrained by the accuracy of the documents rather than the physical state of the component itself.
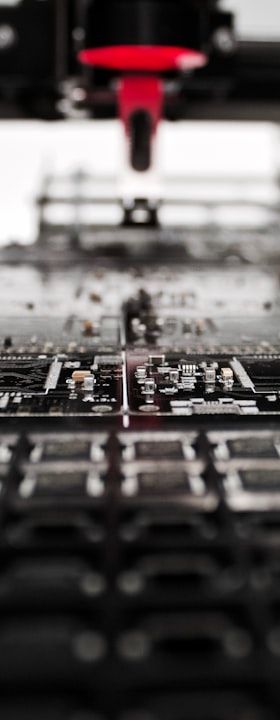
As a response to this gap, Cybord promotes visual AI inspection integrated directly into SMT pick-and-place processes. The approach captures high-resolution images of each component at the moment of placement and analyses them against a reference database to assess authenticity, condition, and provenance indicators. This positions the inspection step not as a separate downstream audit but as an embedded, real-time verification layer within the assembly line.
For European electronics manufacturers supplying U.S. defence, aerospace, automotive, or industrial customers, the CHIPS Act compliance requirements carry practical relevance even outside U.S. jurisdiction. Contract manufacturers and EMS providers operating in the European market increasingly face customer-driven traceability mandates that mirror or reference the CHIPS Act framework, particularly for safety-critical applications.
The paper also highlights the risk profile associated with the current documentation-centric model: fraudulent certificates of conformance and misrepresented component origins are established vulnerabilities in global semiconductor supply chains, well-documented by industry bodies including ERAI and the Semiconductor Industry Association. Counterfeit or substandard components reaching the production line represent both a regulatory and a product-integrity risk.
Cybord's approach aligns with a broader industry movement toward machine-readable, data-driven traceability — a direction also reflected in IPC's Connected Factory Exchange (CFX) standard and ongoing MES integration strategies across European SMT lines. Whether AI-based visual inspection at placement can serve as a legally recognised verification mechanism under CHIPS Act audit requirements remains a question that procurement and compliance teams will need to evaluate in coordination with legal counsel and certification bodies.
Quelle: Cybord – https://cybord.ai/news_events/news/identifying-the-source-of-electronic-components/